Wednesday, July 18, 2018

Amazon Prime Day - Dog Days, PC sales are up First Time since 2012

Amazon's Prime Day starts with a picture of a Dog.

The Amazon Prime Day 2018 got off to a rough start as the sudden rush of online shoppers evidently overwhelmed the servers and shoppers were greeted with pictures of dogs rather than what the products the links promised.  You have probably seen a 404 error page before on the internet when a page you were looking cannot be found.  Amazon presents you with a picture of a dog when you encounter a 404 error on their servers.


I first heard about the issues from an alert client who called and told me about it.  He was online to buy some items we found over the weekend for his system.


The hellish problems continued for hours frustrating many shoppers who have little patience with internet issues to start with.  To exacerbate things, the absence initially of any problems by Amazon contributed to customer anxiety.

Amazon Web Services (AWS) is actually the largest Cloud Provider.  If you are using a Cloud service such as any accounting services (Yardi), health care, or any other hosted internet service, there is a good chance that it is actually being hosted on a server running under AWS.  However, Prime Day woes appeared to be restricted to problems caused by code in the Amazon Store.


As of 3rd Quarter 2017 the 7 largest cloud providers were;

7.  SAP SE - $1.02 billion
6.  Oracle - $1.19 billion
5.  Alphabet (Google) - $1.8 billion
4.  Salesforce - $2.2 billion
3.  IBM - $3.5 billion
2.  Amazon - 3.66 billion
1.  Microsoft - $6.76 billion

The rankings are fluid and change yearly.  In 2015 AWS was number 1.  So far in 2018, Microsoft remains number 1, followed by AWS, Salesforce, IBM and then Google.


PC Sales are up for the first time since 2012

PC sales are posting the first growth in shipments since 2012.  The experts are pegging this growth on demand for desktops by businesses and people looking for high-performance gaming PCs.

What the experts are missing in this equation is Intel Generation 8 processors that offer truly outstanding increases in processing capability.

The Intel Core i3 has gone from 2 cores to 4 cores and now offer an unlocked K version for performance seekers.

The Core i5 and Core i7 processors have both been increased from 4 to 6 cores.

The improved processors combined with the new supporting chipsets are on a new plateau from the previous offerings.

In addition, SSDs have come down in price and it is becoming increasingly affordable to offer an M2 slot 128/256 GB to host the OS for lightning fast startup.


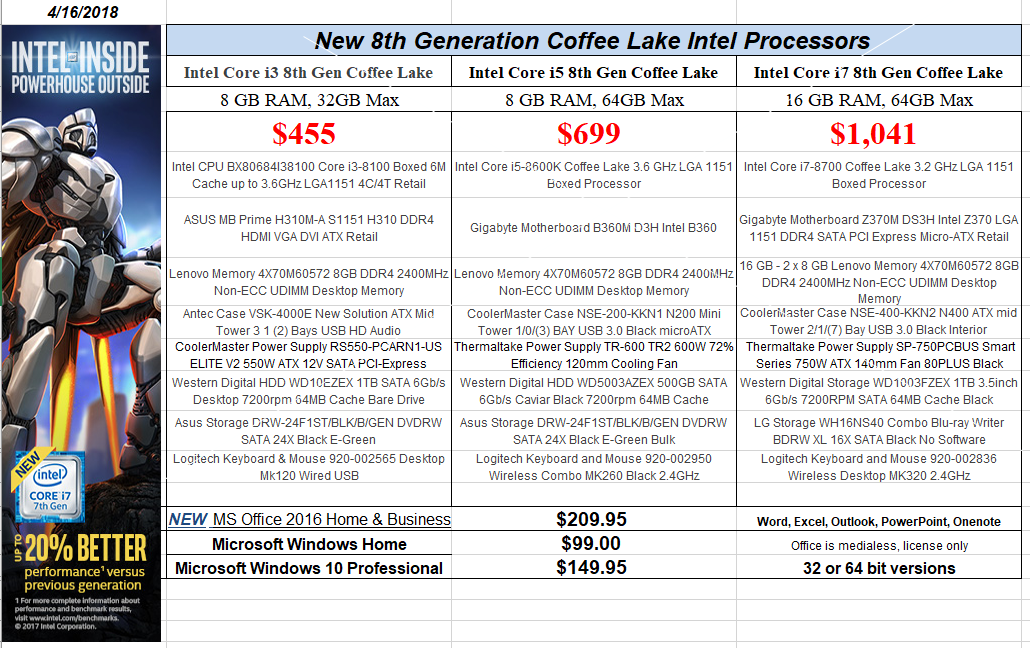
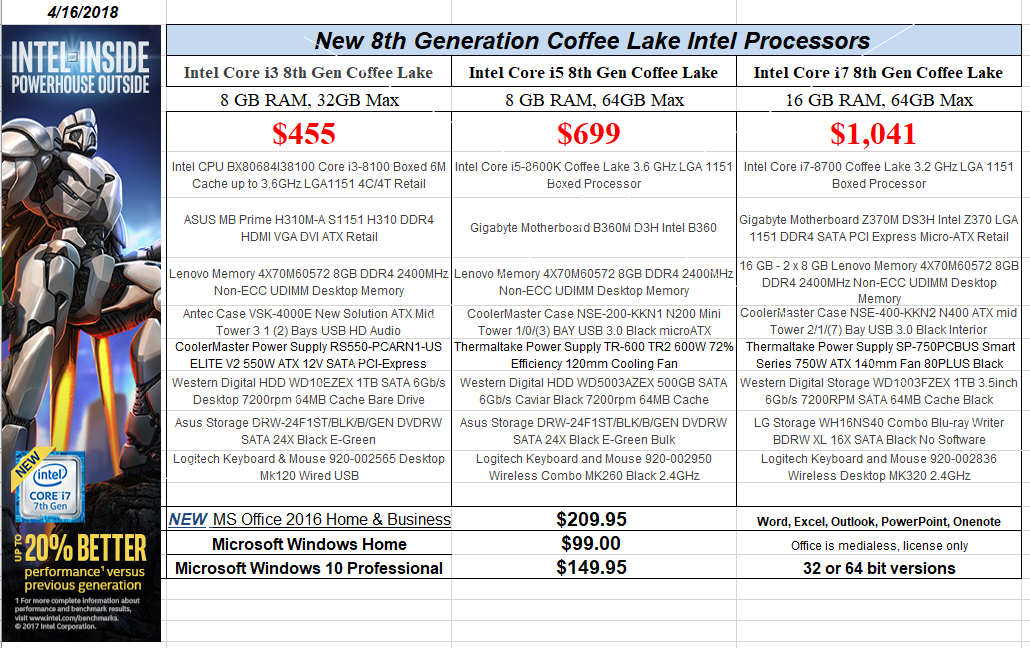
Driving Force offers a full line of Gen 8 workstations to fit any need.  Whether you are looking at the most economical or a powerful platform to last for years to come, any of these will beat your current system.

For pricing please click on image below.  Thanks!


Thursday, June 7, 2018

FBI urges internet users to reboot their routers to stop Russia-linked malware

This news first broke a couple of weeks ago and has been reported by major publications and news networks but the threat is continuing and evolving.  I was contacted yesterday by an alert client who wanted to know if it was legit.  It is and upon further research, I thought I should contact my base and alert anyone who may not have heard about this.  Many of you have affected routers.


The Russians are at it again, the same group that hacked the Democratic National Committee ahead of the last Presidential election in 2016, "Sofacy Group" has released a malware that is capable of disabling an internet router.  The malware is called VPNFilter and it has already affected hundreds of thousands of routers in other countries.  In addition to causing your router to become inoperable, it can collect data and therefore has the capability of stealing logins and passwords.

According to the news release there is no easy way to know if your router has been compromised.  CNET reports that some models from LinkSys, Netgear, TPLink, QNAP, and Mikrotik are affected.

According to CNET;

"The U.S. government says it has seized a critical web domain, called toknowall.com, which the Russian hackers were using to disseminate the malware.
So, now, when you reboot your router, it throws a kink in their system, essentially destroying the part of the malware that allows hackers to spy on your activities. The install package, on the other hand, will be left intact. After a reboot, when that package attempts to download the other nasty parts of the malware, the FBI will be able to trace it."
The article states that the easiest way to restart is by pressing and holding the reset button on the back of the router, however, I would advise caution doing this since performing this on some models can cause a factory reset.  I would disconnect and then reconnect the power to the router myself to reset but it would be best to consult your router's manual.

However, then there is this from the article;

But some security experts advise that a factory-reset is the only sure-fire way to purge VPNFilter from a router. Once that's done, you'll have to reconfigure all your network settings. Check your model's instruction manual for help with both steps.


https://www.cnet.com/news/the-fbi-wants-you-to-reboot-your-router-now-to-help-destroy-a-botnet/

https://www.cbsnews.com/news/fbi-urges-internet-users-to-reboot-home-routers/


more from BGR.com;

The attacks appear to be incredibly targeted, as the hackers are looking for specific things. “They’re looking for very specific things,” Williams said. “They’re not trying to gather as much traffic as they can. They’re after certain very small things like credentials and passwords. We don’t have a lot of intel on that other than it seems incredibly targeted and incredibly sophisticated. We’re still trying to figure out who they were using that on.”

But wait, there’s more. The malware can also download a self-destroy module that wipes the device clean and reboots the device.

Getting rid of VPNFilter isn’t an easy task. The malware is constructed in such a way that a Stage 1 attack acts as a backdoor on devices that can be infected, and is used to download additional payloads, Stages 2 and 3, which bring over the more sophisticated features, including man-in-the-middle-attacks and self-destruction.


All routers owners should assume from the start that their device has been infected, and perform a factory reset, Ars says, followed by a software update that could remove the device’s vulnerabilities to Stage 1 infection. Changing default passwords is also advised, as is disabling remote administration. Rebooting the device like the FBI asked might not be enough, however.

http://bgr.com/2018/06/07/vpnfilter-malware-security-threat-fix/


Apple is facing a Class Action lawsuit over Mac notebooks and more news as Macs continue to fade in performance, reliability and relevance.

https://www.zdnet.com/article/why-wwdc-2018-served-as-macs-death-sentence/?ftag=TRE-03-10aaa6b&bhid=2219791


INTEL Generation 8, a Giant Leap in desktop Power


Tuesday, May 1, 2018

Apple reports quarterly earnings today after the closing bell on Wall Street.  The call will be closely followed by investors concerned about reports of slow iPhone X sales and the resultant reports of drag on earnings at component suppliers of Apple products.

60% of Apples Revenue is from the iPhone as innovation in Macs lags PCs and Apple discontinues other product lines.  The company is hoping to boost revenue through services yet iCloud continues to disappoint.  Their HomePod product (Echo dot/Alexa rival) does not come close to competing yet with Amazon and Google rivals and it's $299 price tag is steep for a speaker.

Amazon Prime is going up 20% in price, from $99 to $119 annually.  Lots of news, please see links below.

Apple earnings report out today.

60% of Revenue from iPhone.

https://www.reuters.com/article/us-apple-results-preview/investors-look-to-apples-cash-services-as-iphone-sales-seen-stalling-idUSKBN1I11XP?il=0


For Apple's iPhone X, is it time for 'full panic mode'?
Apple suppliers are hinting at a rough quarter, with indications people aren’t spending big on the iPhone X.

https://www.cnet.com/news/for-apple-iphone-x-is-it-time-for-full-panic-mode-with-q2-financial-results/?ftag=CAD1acfa04&bhid=21042726186831923270015874178287


Apple officially discontinues AirPort router product line, available while supplies last

https://appleinsider.com/articles/18/04/26/apple-discontinues-airport-base-station-product-line-available-while-supplies-last


iPhone X old news? What that means for new 2018 iPhones
This week was ripe with talk about the rumored iPhone SE 2 and new 2018 iPhones.

https://www.cnet.com/news/iphone-x-old-news-what-that-means-for-2018-iphones/

Apple’s working on a powerful, wireless headset for both AR, VR

https://www.cnet.com/news/apple-is-working-on-an-ar-augmented-reality-vr-virtual-reality-headset-powered-by-a-wireless-wigig-hub/


Why Amazon Is Raising the Price of Prime ... Again
Offering the best deal in retail is getting more expensive every year.

https://www.fool.com/investing/2018/04/27/why-amazon-is-raising-the-price-of-prime-again.aspx

Is Amazon Prime worth its new $119 price tag?

https://www.marketwatch.com/story/is-amazon-prime-worth-its-new-119-price-tag-2018-04-27


New Intel Generation 8 computers


Tuesday, April 24, 2018

The City of Atlanta spent at least $2.6 million on ransomware recovery.

Atlanta spent at least $2.6 million on ransomware recovery
The ransom was never paid because the payment portal was pulled offline by the attacker.

I wonder how much they spend on their IT support people and security software, obviously not enough.


Windows warning: Tech-support scammers are ramping up attacks, says Microsoft
Windows 10 security won't protect you from tech-support scammers' lies and trickery.


Wednesday, April 18, 2018

Chrome Browser 66 rolls out: Autoplay videos silenced by default and a slew of Bug patches


Chrome 66 mutes audio on autoplay video by default unless a user tends to watch video on a site with sound on.

One of the most annoying things I experience when using the internet is the autoplay videos that occur when visiting many sites.  Many times I want to READ the article in peace but there are these background ads or videos that I don't care to watch must less listen to.

In the more recent versions of Chrome, there was a Mute Site option that you could set for each individual website you visited by right-clicking on the Chrome browser tab for the site and selecting Mute Site.  That allowed you to permanently block sound on a site by site basis.  That was a big help, however, have you ever had many instances of Chrome open, needing most of them and all of a sudden sound starts playing and it's difficult to track which tab is playing the video or ad.  I have had to shut down all before, very annoying.

Starting with Chrome 66, it is now an option to block unexpected video playback by default on the first visit to a site.

Google is accomplishing this using technology called MEI, Media Engagement Index.

The MEI gauges users' tendency to consume media on a site and will allow sites to ignore the rule if the user's engagement passes a certain threshold.

In addition to adding this outstanding feature, Chrome 66 brings 62 security patches for previously found bugs.  Google paid $34,000 to researchers who found and reported bugs.  

To read this and more visit;


To download Chrome 66 visit, http://chrome.com  download and install Chrome!

Once you have installed it you can check your version by clicking on Settings in the upper left corner of the Chrome browser,
and select About Chrome.

You can check your Advanced settings by clicking on the 3 vertical dots on the right side of  the Chrome Browser,


and then under Advanced Settings, Privacy and Security, Content settings,


here are some of the sites that I blocked with the previous version;


Remember Safe Surfing!


In addition to the above, here are Five tricks to make Google Chrome faster and better;


Wednesday, April 11, 2018

Intel 8th Gen vs 7th Gen CPUs: Kaby Lake Refresh Is a Lot Faster

The introduction of the new Gen 8 Intel Core series processors has significantly increased the performance of computers.  The number of cores (processors) for all lines has been increased,

the Core i3 has increased from 2 to 4 cores, the Core i5 and Core i7 chips have gone from 4 cores to 6 cores and the enhancements are noticeable in Microsoft Office applications.

Spreadsheets

If you're crunching large spreadsheets with Excel, you want 8th Gen Core. When we ran a macro that matches 65,000 names with their addresses, the 7th Gen-powered Swift 3 finished in 2 minutes and 36 seconds while the new model completed the same task in just 1:32, a 70 percent improvement. The 8th Gen-powered XPS 13 was even quicker, finishing the macro in 1:08, compared to the 7th Gen-powered model's 2:30., a 55 percent jump.


to read about all the improvements and benchmark tests visit:

https://www.laptopmag.com/articles/kaby-lake-refresh-8th-gen-vs-7th-gen

Monday, April 9, 2018

Facebook to let you know if your data was shared with Cambridge Analytica

According to a news report by CNBC, starting today, Monday 04/09/18,  Facebook will display a link at the top of your news feed call "protecting your information."  If your data was shared with Cambridge Analytica, a message above that link will let you know.

So far this a.m. I am yet to see this on my Facebook page.

Facebook disclosed last week that 87 million users' data possibly was compromised.

https://www.cnbc.com/2018/04/09/facebook-to-notify-users-if-data-was-shared-with-cambridge-analytica.html

One thing I did find interesting on my Facebook page was an item called Photo Review which had an alert on it.  I clicked on it and there was a photo which I was in attending a BJJ tournament this spring.  I do not know the person but Facebook had identified me standing in the crowd.


Photo Review shows you photos you might be in, which are found using face recognition technology. 

Now that's some scary stuff.

Other tech news you may want to read,

Facebook disclosed last week that 87 million users' data possibly was compromised.


and this...

A group of protestor's called 'Raging Grannies' have been protesting outside Facebook's HQs.  Not making this up, hahaha!!!!!!


Avoid Windows 10 crapware: How to get rid of Candy Crush and all the rest


The End of Windows
Posted on Monday, April 2, 2018

https://stratechery.com/2018/the-end-of-windows/?utm_source=hackernewsletter&utm_medium=email&utm_term=fav


 8x8 Cloud PBX

Thursday, April 5, 2018

Windows 10 Spring Creators Update - Act fast if you want to DELAY this big upgrade

In the next few weeks, Microsoft will start rolling out the first of two planned major updates in 2018 for Windows 10.  The upcoming update is dubbed the Spring Creators Update and could be available as soon as April 10th.

I am a big proponent of installing updates so that your machine has the latest patches and bug fixes for security sake, however, Windows Updates can be painfully slow and in some cases break your computer.  Another issue is updates are given without warning.  I can't tell you how many times I have been in the process of shutting down my notebook to rush to another client and have received the message, "Installing updates, do not turn off computer".  The new version is supposed to address this along with other issues.  However, if you wish to delay please read the following.

Each time Microsoft rolls out a major upgrade to Windows 10, you have the option to wait a few months before you install it on PCs running Windows 10 Pro or Enterprise. But you have to act quickly.

https://www.zdnet.com/article/windows-10-spring-creators-update-act-fast-to-delay-this-big-upgrade/

I'll give you 3 other examples of my own personal Windows update woes that may give you further reason to delay the planned update.

1.  When I installed last Fall's Creators update on my desktop, I ended up reinstalling Windows 10 & all software after winding up with a mouse cursor, black screens (no icons) and no way to roll back with no solution in sight.

2.  I updated my notebook last week and when finished I had a bubble and unuseable mouse on the screen.  Upon investigating I learned I was not alone, it is an issue with touchscreen computers.  I had to disable my touchscreen to be able to use my notebook.  I am still waiting for a solution to that problem.

3.  Spent 3 hours at my CPA Tuesday updating his computer which was way behind on updates including Fall Creator update.  He had been thwarted from updating his computer by an issue with a  long gone version of Neo 8, disc burning software.  After finding and deleting all references to Neo in the registry and on his hard drives we were ready to update.  Well 1 hour and 45 minutes later his system finished updating and we were out of time to finish my taxes.  Reschedule for this Sunday at 2 pm, at least I have some time to offset his bill.  In hindsight I would have scheduled his computer to update that night but since he had been so long without Windows update working. he wanted to be sure it would update.


Version 1803, coming soon to a Windows 10 PC near you is supposed to help address some of the above issues.

"One of the most common complaints about earlier feature updates is that the update arrives unexpectedly and commandeers the system for an hour or more, usually at a time when the PC's owner is unprepared for it."

This update addresses that complaint in two ways.

First, there are additional options to warn that the update is about to be installed, with options to schedule the installation for a convenient time.


Second, most of the update takes place in the background, which means that the visible port will take less time and allow you to get back to work more quickly.

To read more about these improvements and for a list of improvements and new features please read;

https://www.zdnet.com/pictures/whats-new-in-windows-10-version-1803-the-spring-creators-update/2/


Panera Bread’s data leak might affect more than 37 million customers

It’s getting to the point where no matter what kind of business you conduct, there is a very real risk of seeing your personal information leaked to nefarious parties. So far, hackers have gained access to banking, credit reporting, health insurance, email, and seemingly just about every other modern circumstance where your data is saved in a database. The latest: That soup and salad you ordered online at Panera Bread might have cost you some peace of mind.

Customer data may have been exposed for as long as 8 months before Panera Bread acknowledged the breach.

https://www.forbes.com/sites/leemathews/2018/04/04/panera-bread-exposed-data-on-millions-of-customers-for-8-long-months/nth#217483cc2242

Sears Holding, Delta Air hit by customer data breach at Tech firm

On a smaller scale, both Sears Holding and Delta Air announced data hacks of customer information.  Sears said that less than 100,000 of its customers were affected by the unauthorized access of credit card data.

The breach was supposed to have happened on or after Sept. 26, 2017, discovered and stopped on Oct. 12 according
Both firms used the same technology firm { 24}7.ai for online support services.  The firm was hit by a cybersecurity incident which exposed the customer payment info of their customers.  The firm also provides services to KMart and other customers.  Sears said its stores and internal systems were not affected.

and finally some good news,

IBM says breached records dropped by nearly 25 percent to 2.9 billion last year

https://www.zdnet.com/article/ibm-says-breached-records-dropped-by-nearly-25-percent-to-2-9-billion-last-year/


Korean cryptocurrency exchange boss arrested for fraud

Cryptocurrency continues to fall, Bitcoin now below $7,000 and Ethereum sub $400.  South Korean authorities arrest Coinnest head for embezzlement and fraud. The arrest follows the prosecutors' raid last month of three cryptocurrency exchanges at Yeouido, South Korea's equivalent of the US' Wall Street.

https://www.zdnet.com/article/korean-cyrptocurrency-exchange-boss-arrested-for-fraud/


Intel Generation 8 processors.

Did you know that the biggest advancement in processors occurred with the latest release of the Intel Generation 8 lineup?

Entry level Core i3s now have 4 core processors vs 2 in Gen 7.

Core i5s and Core i7s have 6 core processors vs 4 in previous generations.

Call Driving Force today about upgrading your computers, www.drivingforce.net


Wednesday, March 28, 2018

Facebook announces Privacy-setting changes.


Facebook announces Privacy-setting changes.


Amid the uproar and corresponding drop in the price of its stock, Facebook has redesigned the settings menu on mobile devices to make it easier for users to control.  Previously the settings were spread across 20 screens.  Now you can find all the settings accessible from a single place.

The enhancements include:

New Privacy Shortcuts menu. People have also told us that information about privacy, security, and ads should be much easier to find. The new Privacy Shortcuts is a menu where you can control your data in just a few taps, with clearer explanations of how our controls work. The experience is now clearer, more visual, and easy-to-find. From here you can:

Make your account more secure: You can add more layers of protection to your account, like two-factor authentication. If you turn this on and someone tries to log into your account from a device we don’t recognize, you’ll be asked to confirm whether it was you.

Control your personal information: You can review what you’ve shared and delete it if you want to. This includes posts you’ve shared or reacted to, friend requests you’ve sent, and things you’ve searched for on Facebook.

Control the ads you see: You can manage the information we use to show you ads. Ad preferences explain how ads work and the options you have.

Manage who sees your posts and profile information: You own what you share on Facebook, and you can manage things like who sees your posts and the information you choose to include on your profile.

https://newsroom.fb.com/news/2018/03/privacy-shortcuts/

and,

Playboy Latest to Delete Facebook Amid Data Handling Fallout

Playboy announced its intention to deactivate its Facebook accounts and leave the social network amid escalating concerns about the platform’s mismanagement of user data.

The publisher said that the decision follows the difficulty it has felt for years to express its "values" on Facebook, due to the platform’s policy on prohibiting nudity.


https://www.bloomberg.com/news/articles/2018-03-28/playboy-latest-to-delete-facebook-amid-data-handling-fallout

Six days after a ransomware cyberattack, Atlanta officials are filling out forms by hand

In the past year, the City of Atlanta has experience 124 malware attacks per day, which equals 45,579 a year.  20 attacks were successful which shows that no matter what methods you employ to prevent a successful exploit, the weakest link is in the seat.  1 breach can spread to thousands of computers and that is the task security experts and techs are now having to perform.  The task of checking servers, desktops, and notebooks could take weeks if not months to complete.

If the city were to pay the $50,000 in cryptocurrency to the criminals it has to be sure that all computers are clean of the malware to prevent it from being held hostage again after payment.

Now it appears that another metro area city has the same problem.  Loganville on Monday said that an attack on a city computer may have compromised personal information.

A post on the city's Facebook page spelled out there is no evidence the hackers took information that would include Social Security numbers and financial account numbers but acknowledged whoever pulled off the attack, would have had access to such information.

http://accesswdun.com/article/2018/3/652779/loganville-city-government-victim-of-cyber-attack

Friday, March 16, 2018

Office 365 and Cloud Security - Passwords

Office 365 is a great product and the subscription model provides services and up to date software on an affordable monthly basis.  It like other cloud services have become the norm for a lot of businesses as internet speed approaches what use to be the standard for in-house LANs, 100 Mbps.

It is this connection speed that has allowed the "cloud" to become ubiquitous in today's business climate.  But the cloud is not some magical new device, it is actually a server owned by someone else located somewhere else.  In the past it was imperative we protect a business server from attack via strong passwords, firewalls and/or virus software.  Hackers were searching public IP addresses for Exchange, SQL and other servers to attack.  They still are and Office 365 is a prime target.  Although the online services scan the incoming email for malicious content, not all is prevented from getting through.  Users constantly receive email phishing attempts trying to coerce them out of their login info by verifying the account to a bogus link.

I have one client who I provide accounting software/services who use Office 365 purchased by their in-house IT department.  He told me the phishing/spam seemed to increase when they switched to the online service.  They too had an account hacked in an attempt to steal money.

In the past month, 2 different clients of mine had their Office portal passwords compromised.  These were not obvious passwords either.  In one case the hacker worked silently and studied the email in the inbox gleaning the firm's banker information and other data that could be used for financial gain.  The hacker then created inbox rules so that any incoming emails that contained information related to the banker's email address or containing words such as "wire transfer" was forwarded to a Gmail account and then deleted so the compromised account holder wasn't aware of his actions.  The information gathered allowed the hacker to act on behalf of the compromised user for certain actions.  The hacker then attempted a wire transfer which the alert banker was suspicious of because the signature block was normal and it was not the standard operating procedure for the firm.

When I was contacted we immediately changed her portal password and upon analysis of the email determined the origin of the IP address was Nigeria.  Changing the password stopped any further meddling by the hacker but we still did not know about the rules the hacker had created.

The company also used an online recruiting firm to fill positions in the firm.  The hacker had created a rule to divert email from the recruiting agency to the Gmail account and then delete the email to hide his actions.  Next, the hacker requested a password reset which was forwarded to the Gmail account.  The password was changed thus allowing the attacker access to the firm's account with the recruiting firm.

This was discovered when an applicant contacted the firm about a position that was advertised online.  When the administrator attempted to log in the password did not work.  After multiple requests for a password reset the administrator discovered the password reset emails in her deleted items.  The hacker's reward was a charge to a credit card with funds diverted to the hacker.

In the second case, the compromised account was used to spam email containing a link to a malicious payload to anyone who clicked on it.  It was disguised as a Purchase Order needing approval.  In this attack, the hacker had created rules to delete any returned emails marked as "Undeliverable" to hide the fact that the account was being used to send spam.

Solutions:

Since the attack. we have changed all passwords at the first client using passwords generated by Microsoft and reimplemented the policy of changing passwords every 90 days.

I hear a lot of complaints about having to use/change passwords but in today's online environment it is imperative that you use strong passwords, change them periodically and do not use the same password for everything.  If you have your email account hacked, I know you do not want to run the risk your banking account is now vulnerable.

If you have a lot of passwords and find the task too frustrating to maintain, consider a password management software such as dashlane or Lastpass to help.  For an annual fee, you will only have to remember 1 password, the master password to the password manager itself.  Below is a link to an article about the best password managers for 2018.

https://www.tomsguide.com/us/best-password-managers,review-3785.html


Crypto-currency News

oh man! crypto-currencies continuing to tank. Be careful trying to catch a falling knife. I'm looking to get back in, it's hard to get into Ripple XRP, my experience.

https://www.cnbc.com/2018/03/15/bitcoin-price-over-60-billion-wiped-off-value-of-cryptocurrencies.html

https://www.politico.com/magazine/story/2018/03/09/bitcoin-mining-energy-prices-smalltown-feature-217230

https://www.msn.com/en-gb/news/world/a-new-york-town-just-placed-a-moratorium-on-crypto-mining/ar-BBKiZdv


New Intel Gen 7 & Gen 8 computers!

Cloud PBX services

TEST