Thursday, May 19, 2022

10 things that let cyber criminals in.

In today's cyber threat environment prompted by economic conditions and amid today's heightened geopolitical tensions due to Russia's invasion of Ukraine, cybersecurity has taken on renewed urgency.

The US Cybersecurity and Infrastructure Agency (CISA) and it's peers around the world have created an issued a list of concerns that prioritize things companies and individuals can do to minimize threats to systems.  This list is called Alert (AA22-137A).

  • Multifactor authentication (MFA) is not enforced.
  • Incorrectly applied privileges or permissions and errors within access control lists. 
  • Software is not up to date.
  • Use of vendor-supplied default configurations or default login usernames and passwords.
  • Remote services, such as a virtual private network (VPN), lack sufficient controls to prevent unauthorized access. 
  • Strong password policies are not implemented. 
  • Cloud services are unprotected. 
  • Open ports and misconfigured services are exposed to the internet.
  • Failure to detect or block phishing attempts.
  • Poor endpoint detection and response.
What should you do?  The italicized items above are within your control.

Multifactor authentication (MFA) or two step is a must for those using SaaS or cloud access services.  Many users consider it an annoying additional step but it is necessary to secure and protect cloud services and assets.  What it does is require one to receive a code via text or email when trying to access the service.

If you or a user's credentials are compromised via phishing or malware the hacker can then access the compromised account from any connected device and cause havoc via using the account to send spam emails phishing for information or carrying malicious attachments.  In addition, they create rules diverting critical emails from financial institutions to their own external email accounts.

What's more, once in they have access to OneDrive and SharePoint documents.  Using this data they can glean information about finance and uncover personal information about other users, staff and clients.

Even worse, an attacker could upload files containing malicious software that can spread to other systems.  Worse yet, Ransomware could be deployed and all of a company's data could be encrypted and held ransom by the attacker.

MFA is becoming a prerequisite required by insurance companies who provide coverage against damage caused by cyber attackers.

If your company has MFA implemented none of the above can happen since the attacker cannot access the compromised account without the code that is delivered via text or a secondary email account.

Software is not up to date.  Because of non patched systems, even MFA was compromised.  Last year Russian hackers combined a default policy shared by multiple MFA solutions and a Windows printer privilege of escalation flaw to disable MFA for active domain accounts and then establish remote desktop protocol (RDP) connections to Windows domain controllers

Be sure to keep your computers and devices updated.  Check and make sure Windows Update is running and apply updates when available.

Use of vendor-supplied default configurations or default login usernames and passwords.  Routers, switches, printers and other devices are delivered with User names and passwords to prevent access to the device and the underlying network.  These credentials are the same for all of a manufacturer's products and readily available via a Google search online.  Discover what your device's credentials are and change them.  You can do this generally via a browser interface using the IP or Mac address or the device.

ISPs, internet service providers routers and equipment are guilty of this as well.  Comcast, AT&T have public IP addresses that can be used to access and exploit the device using these credentials.  Linksys, Netgear and almost all consumer routers are guilty as well.

Strong Passwords.  Too many users take password policy lightly.  Avoid using dates that coincide with life events, i.e. birthdays, anniversaries, etc.  Do not use consecutive numbers and when strong passwords are established, avoid changing a good password by adding a one when it expires, example, Zav98721 to Zav98722.  Attackers and their algorithms are wise to this and once a user and compromised password on on the dark web, an attacker will try this.  For more info on creating strong passwords, see my previous blog post from March 7, 2022.  

https://dforceatl.blogspot.com/2022/03/httpswwwcnbccom20220227most-common.html

For more info on securing your computer and network environment, use the following link to the full article;

https://www.zdnet.com/article/fbi-and-nsa-say-stop-doing-these-10-things-that-let-the-hackers-in/?ftag=TRE-03-10aaa6b&bhid=%7B%24external_id%7D&mid=%7B%24MESSAGE_ID%7D&cid=%7B%24contact_id%7D&eh=%7B%24CF_emailHash%7D


Monday, March 7, 2022

Password Security, Windows 10 settings that need to be turned off, Chromebook use by Date

Good morning.  In today's blog,

- These are the 20 most common passwords leaked on the dark web — make sure none of them are yours

With no end in sight for the Ukraine/Russia conflict and the threat of Russian cyber warfare, it is important for everyone to assess their password strategy to secure their online data.  see below for more info.

- Turn Off These Annoying Windows 10 Settings

One of the default settings in Windows 10 allows Microsoft to use your computer to provide updates to other users on the web?  That's right, your computer and internet connection are being utilize world wide as an update server.  See this section below for more information.

- Before You Buy a Chromebook, Check the Expiration Date

Are you considering buying a Chromebook?  Be sure to check your expiration date.  Who'd have thought, Chromebooks have a use by date?

https://www.wsj.com/articles/before-you-buy-a-chromebook-check-the-expiration-date-11646538322?st=8yr80fa3kya5zw5&reflink=desktopwebshare_permalink


These are the 20 most common passwords leaked on the dark web — make sure none of them are yours

CNBC has published a list of the top 20 passwords found on the dark web.  Many of these I have seen in use or a slightly different version from some of those listed.

Password security is a pain I know but it is your only defense in protecting your financial and personal data from being stolen and causing much more pain.

Some of the things you can do is change your passwords on a regular basis and do not reuse passwords either on the same account or use the same password for multiple accounts.  The first thing hackers will do once they have compromised one of your passwords is to try that password on your other accounts.

If you change your password do not perform a simple change such as adding 1 to a number, i.e. Blah987 to Blah988.  They know this trick.  They are equipped with powerful cracking programs that can perform millions of combinations and permutations of passwords based on a cracked password in minutes.  With many computers and lots of compromised systems working for them, they have time on their side.

To see the 20 most compromised passwords, follow the link below and then check the chart below to see how your password stacks up for complicity.

 Most common passwords hackers leak on the dark web: Lookout report (cnbc.com)

If your password wasn't on the list above then just how safe is your current password?  The chart below project just how long it would take a computer to crack your password.

The Y axis depicts the length of your password while the X axis lists complexity.


Turn Off These Annoying Windows 10 Settings

Did you know the default setting in Windows 10 allows Microsoft to use your computer to provide updates to other users on the web?  That's right, your computer and internet connection is being utilize world wide as an update server.

Microsoft plans to roll out Windows 11 to all eligible computers by mid 2022.  That said, if you have a computer that does not meet the hardware requirements to upgrade or prefer to stay with Windows 10 then read the following article and change these settings to improve your computer performance and Windows 10 experience.


DForce Intel based Windows 11 Workstations


Wednesday, February 16, 2022

Chrome Zero-Day Under Active Attack: Patch ASAP

 Chrome Zero-Day Under Active Attack: Patch ASAP

Google's Chrome, the popular web browser has a critical flaw that is currently under active attack by bad actors.  The flaw is classified as a zero day (active attack) bug and the patch needs to be applied immediately.

In a brief update, Google described the weakness, tracked as CVE-2022-0609, as a use-after-free vulnerability in Chrome’s Animation component. This kind of flaw can lead to all sorts of misery, ranging from the corruption of valid data to the execution of arbitrary code on vulnerable systems.

https://threatpost.com/google-chrome-zero-day-under-attack/178428/

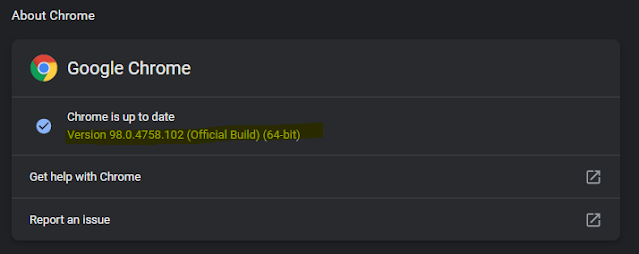
The fix is to update Chrome browser to the latest version 98.0.4758.102.  This will resolve this issue along with 10 other security issues.

The affected OSs include MAC, Linux as well as Windows users.

To check your Chrome version and update do the following,

Click on Chrome Menu buttons at top right of browser and select Settings,


Next select About Chrome at the bottom


Check your version and make sure it is 93.0.4758.102.  If not update.


That is all. Happy Hump Day!

buy a computer!  DForce Intel 11th Generation Workstations


Wednesday, February 9, 2022

Microsoft Patch Tuesday-February 2022 and Windows 11

Yesterday was Patch Tuesday so many of you may be seeing the Windows 11 upgrade offer or a message saying your computer doesn't meet minimal requirements. Windows 11 requires TPM 2.0 (Trusted Platform Management), UEFI and Secure Boot enabled. If you have an older machine then you will probably not be eligible for the upgrade. It is estimated that 55% of existing Windows computers will not be Windows 11 compatible.  There may still be hope if you want Windows 11 however... discussed later in post.

If you are running Windows 10, Microsoft has issued updates to patch several security flaws, none deemed critical but Microsoft considers them to be ripe for exploitation.  One CVE-2022-22005 affects SharePoint which is critical to many users and organizations who utilize cloud access.

For a full list of Windows 10 patches please click the following link;


Last Gasp for Windows 11 wannabes!

Despite a message that your machine is not compatible, you may still be eligible by tweaking your BIOS settings.  It may require a BIOS (firmware) upgrade but many machines have a TPM software feature that needs to be turned on and UEFI/Secure Boot enabled.

For a list of all the minimum requirements for Windows 11 click the following link; 


If you are already running Windows 11, the current Patch contains all the fixes from previous updates including a speed boost that corrects a bug that made drive write/read speeds slower.

Known issues (famous last words)

Microsoft is currently not aware of any critical issues in this release, but you should watch for a weird bug where recent emails might not appear in the search results of Outlook desktop app. This bug affects POP, IMAP, Microsoft Exchange and Microsoft 365 accounts.

There’s always a possibility that the Windows Update could break your device. In the past, some updates have caused major issues including Blue Screen of Death errors and problems running certain apps.

For a full list of bug fixes and improvements for Windows 11 in this Patch Tuesday release, please click on the following link.  It also contains links to the full install of Windows 11 which you can use to upgrade if you wish.


DForce Windows 11 workstations


Tuesday, December 14, 2021

Kronos HR Management Platform hit by Ransomware

Kronos hit with ransomware, warns of data breach and 'several week' outage
The HR management platform has already informed major customers, like the city government of Cleveland, about the attack.

Krono's software is used by many major corporations and local governments.  Among it's many clients, Tesla, City of Cleveland, hospitals and universities including Clemson, Temple and Winthrop University Hospital.  The clients use Kronos work management software.

The ransomware attack has compromised employee information including names, addresses and social security numbers.

Worst of all is the outage is going to cause many to miss payroll this week.  Not a pleasant thing during the holiday season.


These researchers wanted to test cloud security. They were shocked by what they found.

Cybersecurity researchers set up a tempting cloud honeypot to examine how cyber attackers work.

Cloud computing has become ubiquitous in business today.  The problem is the same lax password requirements and slack security is being utilized by many of the companies.  Recently cybersecurity experts at Palo Alto Networks set up a honeypot of 320 entry points around the world.  A "honeypot" is similar to a sacrificial lamb and is meant to attract cybercriminals.

The honeypot was designed with weak passwords used default passwords that was shipped from factory, info readily available online.  The honeypot was made up of common remote services, misconfigured to attract malicious actors.

And it wasn't long before cyber criminals discovered the honeypot and looked to exploit it -- some of the sites were compromised in minutes while 80% of the 320 honeypots were compromised within 24 hours. All of them had been compromised within a week. 

"The speed of vulnerability management is usually measured in days or months. The fact that attackers could find and compromise our honeypots in minutes was shocking. This research demonstrates the risk of insecurely exposed services," said Jay Chen, principal cloud security researcher at Palo Alto Networks. 


Intel 11th Generation based Workstations by Driving Force


Monday, December 13, 2021

Tech Giants Microsoft, Amazon and Others Warn of Widespread Software Flaw

This new flaw is called Log4Shell and it allows an attacker to gain entry into servers and computer systems without a password.  Within 12 hours of the Log4Shell exploit being found, hackers were already exploiting the vulnerability online.  Cybersecurity researchers say they have seen thousands of attempts to exploit the bug.

Online Gaming sites are being exploited and any Cloud software entity is at risk.  Amazon, Twitter and Cisco Systems are all working to protect users and study the threat against their systems.

Hackers started exploiting the recent flaw early Friday to gain access to servers running Microsoft’s  Minecraft gaming software.  Security experts noticed the flaw being exploited in Minecraft when players utilize chat features.  A few lines of text passed among players can penetrate the defenses of a targeted computer.  The text is part of Log4J and open source java based logging utility.

Soon they observed widespread scanning and attempts to trigger the Log4j bug across the internet. In a note published Friday, Microsoft advised Minecraft users to upgrade their software to patch the bug.

IBM's RedHat and Oracle's VMware are deploying patches.  The flaw allows attackers to convert computer's log files (files that track a computer's activities) into malicious instructions forcing the machine to download software.  Once this has happened an attacker has access to a victim's network.

Be aware that the threat is against all Internet entities and the problem is that each individual enterprise will have to patch their servers and systems.  Some companies have already begun patching systems but this is not a coordinated simultaneous fix so some users will be at risks longer.

Roblox a popular gaming platform was mentioned on the news this a.m.

Massive data breaches have become so common that we’ve gotten numb to reports detailing another hack or 0-day exploit. That doesn’t reduce the risk of such events happening, as the cat-and-mouse game between security experts and hackers continues. As some vulnerabilities get fixed, others pop up requiring attention from product and service providers. The newest one has a name that will not mean anything to most people. They call the hack Log4Shell in security briefings, which doesn’t sound very scary. But the new 0-day attack is so significant that some people see it as the worst internet hack in history.

“The internet’s on fire right now,” Adam Meyers told AP News. “People are scrambling to patch and all kinds of people scrambling to exploit it.”  Meyers is the senior vice president of intelligence at Crowdstrike, a cybersecurity company monitoring the Log4Shell hack. 

https://bgr.com/tech/internet-is-scrambling-to-fix-log4shell-the-worst-hack-in-history/

Because the bug is easy to exploit and attacks hard to block, the Log4j problem could be used by hackers to break into corporate networks for years to come, said Aaron Portnoy, principal scientist with the security firm Randori. “It is one of the most significant vulnerabilities that I’ve seen in a long time,” he said.

https://www.wsj.com/articles/tech-giants-microsoft-amazon-and-others-warn-of-widespread-software-flaw-11639260827?mod=hp_lead_pos10


DForce 11th Generation Intel unlocked Beasts!

Friday, December 3, 2021

Over a Million WordPress sites Hacked and Chip Shortage-Sky High Video cards prices - Crypto Mining

Over a million WordPress sites breached

UPDATED: WordPress site owners hosted by GoDaddy have had their data exposed -- for months.

https://www.zdnet.com/article/over-a-million-godaddy-managed-wordpress-sites-cracked/

and my experience Crypto Mining

Alleged Chip Shortage and how to become a Crypto Millionaire or not.

The chip shortages affecting automobile production and computer pricing has been in the news lately.  We've been told lots of stories about the cause whether it's supply chain issue or pandemic related.  The chips related to auto manufacturing are supposedly low profit margin and the chip makers are not thrilled about gearing up capacity to supply the auto makers.  Ford is building a plant to make their own chips in the future.  Tesla seems to be the only auto manufacturer not affected.  I'm sure Elon Musk had already incorporated chip manufacturing in the company SOP.

Computer chips have steadily crept upward in prices, especially memory.  The computers Driving Force builds are 99% for business and don't require dedicated Graphics cards for business/cloud applications.

I recently built a new monster PC for myself so I could install/test Windows 11.  At the time there were no video cards available so I had to use an older Nvidia 750 ti card.  I thought Gamers were eating up the available supply of video cards causing shortages and steep prices.  I tried searching for video cards with at least 4GB, preferably 6 GB of memory and they are sold out everywhere.. Best Buy for example.  In addition, the price has doubled at least.  In July of 2019, I bought a NVidia 1650/4 GB Ram for $149.99 at Micro Center.


Today the same card will cost you at least $319 at Newegg, up to $390 for the same chipset.


and those are not the most expensive cards either, see below.


As I said above, I thought it was gamers causing the video cards to be scarce and the chip shortage but I was wrong.  If you watch the stock market you know Nvidia and AMD stocks are some of the hottest ones to have.  Both companies make GPUs, Graphic Processing Units and are experiencing no chip shortage.  

The demand behind their products is Crypto Mining.  That's right, GPUs are more efficient at processing crypto transactions (mining) than computer CPUs.  I've a couple of SOL (Solana) mining machines running full time at my office, one is employing the Nvidia 1650 in my main machine and the other miner is a 3rd generation Intel Core i5 processor.  I had my monster AMD Ryzen 9 mining but the strain mining placed on the CPU was too high.  It affected performance significantly as well as generated a lot of heat from the processor.  I didn't want to risk the investment in my new AMD Ryzen 9 Windows 11 machine, mining is not lucrative enough with my present setup.

However, with the right video cards and enough of them one could make a lot of money mining.  That is why so many countries and even towns in certain US states have outlawed crypto mining.

As of today  12/3/21 at 6:30 a.m. EST, since 11/29/21 11:45 a.m.  I have mined almost $2 ($1.85 to be exact) of Solana, LOL.

There has been some down time.  My initial rig was my AMD machine,  I took it offline and established my main computer with the Nvidia 1650 as a miner.  (BTW, since I don't game I don't see much performance degradation using the GPU rather than the CPU), and yesterday I added a second miner using the old Intel Core i5 computer that plods along in another room happily mining.

So there you have it.  Why there is a chip shortage, 
  1. Chip manufacturers want to build GPUs, not low profit margin auto chips (now even Intel is developing a graphics chip).
  2. GPUs in high demand by Crypto miners.
and that's my story, I'm sticking to it.

I will follow up with another article soon about my mining software and how to build your own mining rig. Also hopefully an update on extreme earnings if I can acquire the right video (GPU) card.  I want to try an ETH Ethereum miner, BTW, Solana which is currently at $236/coin is an Ethereum based alt coin.


Monday, November 8, 2021

Machine Performance suffering, try closing Chrome. Apples and PCs.

I have advised my clients for a year now to try the newest version of Microsoft Edge over Google's Chrome.  Microsoft has rewritten the Edge Browser using the same language, Chromium as the Chrome browser is written in.  This allows Edge to make use of the extensive library of extensions that have been written for Chrome.

There are more compelling reasons to use Edge or some other browser rather than Chrome.  At times my desktop computer's performance became sluggish to the point of "not responding".  What I have found is if I close Chrome the computer's performance returns.  I have multiple displays (3) and run multiple browsers, chiefly Edge, Chrome and Mozilla Firefox.  Recently I have installed the Brave browser and cut my use of Chrome.

I am writing this blog using Chrome (BlogSpot is Google's free blog), and when I check my system resources in use I find that Chrome is using more resources than Edge even though I only have 3 tabs open compared 9 tabs in Edge that are monitoring streaming data from various sites, see below.


Chrome has become bloated and now suffers the same performance issues as Microsoft's old Internet Explorer which killed Netscape and became the browser of choice in the 90's.

Microsoft's Edge is leaner and has released new features such as Vertical Tabs which I love on a widescreen monitor.

ZDNet has recently addressed Chrome's performance woes.  Below are several links that should help you evaluate you own situation.

As always, thanks for reading.  I hope you find it informative.  Also, this issue applies to Apple computers as well as PC as mentioned in the first article.

Dumping Google Chrome? Here's the best browser to replace it

It seems that to quite a few of you, the idea of dumping Google Chrome for a browser -- even if that browser is better -- is like pulling wisdom teeth. Despite the fact that it's a bottomless pit when it comes to eating system resources and has become the bloated browser it was initially meant to replace, people love it.

https://www.zdnet.com/article/dumping-google-chrome-heres-the-best-browser-to-replace-it/

Ditching Google Chrome was the best thing I did this year (and you should too)

It was about a year ago that I began my transition away from Google Chrome (spoilers, I still need to use it, but I now use it minimally).

I disentangled my data and passwords out of the browser.  I tried a whole bunch of other browsers.  I learned and relearned a whole bunch of new muscle memory movements.

It was hard.  But it was worth it.

https://www.zdnet.com/article/ditching-google-chrome-was-the-best-thing-i-did-this-year-and-you-should-do-the-same-too/

Bye-bye, Chrome: 10 steps to help you switch to Microsoft's new Edge browser

If you've been looking for an option to dump Google's Chrome browser, consider Microsoft's new Edge browser, which delivers much of the same experience you get from Chrome, with a few features that are downright superior. Here's how to get started.

https://www.zdnet.com/article/bye-bye-google-chrome-10-steps-to-help-you-switch-to-the-new-edge-browser/


DForce Workstations - Windows 11 is now available on fast, reliable DForce Workstations 

DForce workstations feature matched Processors, Mainboards and SSDs to allow you to maximize performance.  Don't make the consumer based 6 month mistake, fast now, slow later.


Wednesday, June 2, 2021

June 8th: Amazon Sidewalk set to automatically share your internet with neighbors.

WHAT COULD POSSIBLY GO WRONG? —

Amazon devices will soon automatically share your Internet with neighbors.  Amazon's experiment wireless mesh networking turns users into guinea pigs.

If you have an Amazon Echo Dot, Show or any other Alexa activated device, you have less than a week to opt out of having your internet bandwidth automatically shared by Amazon in a huge mesh network.

On June 8th, unless you opt out by changing your default settings on your Amazon devices; The program known as "Amazon Sidewalk" will share your internet connectivity with those who do not have internet as well as allowing you onto your neighbor's connection.

From the Amazon Sidewalk webpage:

Amazon Sidewalk is a shared network that helps devices like Amazon Echo devices, Ring Security Cams, outdoor lights, motion sensors, and Tile trackers work better at home and beyond the front door. When enabled, Sidewalk can unlock unique benefits for your device, support other Sidewalk devices in your community, and even locate pets or lost items.

The benefits of Amazon Sidewalk

Amazon Sidewalk creates a low-bandwidth network with the help of Sidewalk Bridge devices including select Echo

and Ring devices. These Bridge devices share a small portion of your internet bandwidth which is pooled together to

provide these services to you and your neighbors. And when more neighbors participate, the network becomes even

stronger.

Devices in the program include not only Amazon's Echo dots and other smart speakers but Ring doorbells, security cams, Tile Trackers as well as others.

Amazon cites the amount to be shared will be 1/40th of your bandwidth, (80kbps typical internet connection) and will cap the amount of shared bandwidth at 500 MB (megabytes)/month.

Considering that few users ever look at or know how to access the default settings of their devices, expect nearly full coverage.

Amazon has published a white paper detailing the technical underpinnings and service terms that it says will protect the privacy and security of this bold undertaking. To be fair, the paper is fairly comprehensive, and so far no one has pointed out specific flaws that undermine the encryption or other safeguards being put in place. But there are enough theoretical risks to give users pause.

TO read more, click on the following links;

https://arstechnica.com/gadgets/2021/05/amazon-devices-will-soon-automatically-share-your-internet-with-neighbors/

Amazon's Sidewalk Project

Amazon White Paper


Friday, May 28, 2021

SolarWinds hackers are at it again, targeting 150 organizations, Microsoft warns

SolarWinds hackers are at it again, targeting 150 organizations, Microsoft warns

Microsoft has reported that the same group responsible for the SolarWinds attack "Nobellum" are at it again, this time distributing intrusion software via email purporting to be from USAID, US Aid organization.

This time they have compromised email systems linked to the State Department’s International aid agency to send spear phishing emails targeting agencies and individuals who have been identified as anti-Putin.  It is using a message purporting to be from former President Trump with a bait link about election fraud.

If clicked the link delivers malicious files to compromise your system.  

It is reported that the targets are agencies and individuals who are anti-Putin.  The email has a headline that proclaims, (see picture below, courtesy NY Times);

The hackers are linked to Russia's main intelligence agency and the emails are being sent via the email system used by the State Department's international aid agency.

Hackers linked to Russia’s main intelligence agency surreptitiously seized an email system used by the State Department’s international aid agency to burrow into the computer networks of human rights groups and other organizations of the sort that have been critical of President Vladimir V. Putin, Microsoft Corporation disclosed on Thursday.

To read more please visit the links below;

https://www.nytimes.com/2021/05/28/us/politics/russia-hack-usaid.html

https://www.nbcnews.com/tech/security/solarwinds-hackers-are-it-again-targeting-150-organizations-microsoft-warns-n1268893


If you don't have protection, please consider doing something,

https://www.malwarebytes.com/pricing/


TEST