Monday, July 29, 2019

Louisiana governor declares state emergency after local ransomware outbreak

The Governor of Louisiana has declared a statewide emergency after 3 school districts have been hit by ransomware.  The attack has taken down IT networks and their files have been encrypted rendering them inaccessible.

Last year the Governor of Colorada activated a state emergency after the Colorado DOT was shut down due to SamSam ransomware.

Read the entire article at:

https://www.zdnet.com/article/louisiana-governor-declares-state-emergency-after-local-ransomware-outbreak/


IRS warns thousands of cryptocurrency holders to pay their taxes

Did you make a bundle on Bitcoin or some other Cryptocurrency last year?  Uncle Sam wants his cut so get ready to pay up.

https://www.msn.com/en-us/money/markets/irs-warns-thousands-of-cryptocurrency-holders-to-pay-their-taxes/ar-AAEUqU2


Apple News

Apple 15-inch MacBook Pro (2019) review: 8-core power and portability, at a price

https://www.zdnet.com/product/apple-macbook-pro-15-inch-2019/?ftag=TRE0fb9d06&bhid=2219791


At $249, this iPad may be a great deal (or about to be discontinued)

Apple slashes the price of iPad as people are balking at paying high prices.  Apple's new MacBook Air is significantly slower than the older model it replaces.

https://www.zdnet.com/article/at-249-this-ipad-may-be-a-great-deal-or-about-to-be-discontinued/


DForce Intel Gen 8 & 9 based workstations with SSDs


Tuesday, July 9, 2019

Microsoft warns about Astaroth malware campaign, Hackers steal $3 million from Bank in Bangladesh.

Microsoft warns about Astaroth malware campaign

New hard-to-detect Astaroth campaigns spotted using fileless execution and living-off-the-land techniques.

Malware writers have found a new way to circumvent your anti-virus software.  They are using a technique called "living off the land."  This involves using legitimate tools to download code and process the illegal activity completely in the memory of the computer without using files.

The Microsoft Team behind Windows Defender ATP spotted the attacks.  A member of the team said they were alerted when a huge and sudden spike in usage of the WMIC tool, "Windows Management Instrumentation Command-Line" tool.  WMIC is a powerful tool that complements the existing management and administration utilities and tools.  It is a command line shell much like the CMD command.

The sudden spike was indicative of a pattern that occurs during malware campaigns.


When Microsoft looked closer, it discovered a malware campaign that consisted of a massive spam operation that was sending out emails with a link to a website hosting a .LNK shortcut file.

If users were careless to download and run this file, it would launch the WMIC tool, and then a plethora of other legitimate Windows tools, one after the other.

The tools would all download additional code and pass their output to one another, executing solely in memory -- in what's called fileless execution -- and without saving any files on disk, making the job of classic antivirus solutions harder, as they would have nothing to file on disk to scan.

What is a .LNK file, these are files that point to the location of an executable file typically located on a hard drive.  Your desktop shortcuts are examples of this.  However in the case of the malware email, the .LNK file points to a URL on the internet where the malicious file is stored.

The end result of this attack is that the Astaroth trojan is downloaded and run.  It is a known info-stealer that can dump credentials for a wide category of apps and uploaded the stolen data to a remote server.

This trojan first appeared in 2018.  Earlier this year it was used in malware attacks targeting European and Brazilian users in February, this year.

The next step in the evolution of modern antivirus products is shifting from a classic file signature detection mode of operation to a behavioral-driven approach, where they can also detect "invisible" actions like fileless (in-memory) execution and living-off-the-land techniques where legitimate tools are abused for bad operations.

Be very careful opening emails from people you do not know, especially those containing links to external sites.

To read the full story click on this link;

https://www.zdnet.com/article/microsoft-warns-about-astaroth-malware-campaign/?ftag=TREc64629f&bhid=2219791


In other hacking and malware news;

Sodinokibi ransomware is now using a former Windows zero-day

The Sodinokibi malware uses a former Windows Zero-day vulnerability to carry out its attack on infected hosts.

The vulnerability, a privilege escalation flaw known as CVE-2018-8453, had been patched in the October 2018 Patch Tuesday Microsoft security updates after it had previously been used by a state-sponsored hacking group known as FruityArmor since August 2018.

I know updates can be a pain but with so many ransomware attacks occurring today, it is imperative that you patch/update your systems so they remain safe from attack.

https://www.zdnet.com/article/sodinokibi-ransomware-is-now-using-a-former-windows-zero-day/

'Silence' hackers hit banks in Bangladesh, India, Sri Lanka, and Kyrgyzstan, allegedly stole $3 million from Bangladesh's Dutch Bangla Bank.

In a report shared with ZDNet prior to publication, Group-IB tied the Dutch Bangla Bank incident to a group of hackers known as "Silence."


The group, which ZDNet previously covered in a September 2018 piece, has been active since 2016 and has historically targeted banks in Russia, former Soviet states, and Eastern Europe.

https://www.zdnet.com/article/silence-hackers-hit-banks-in-bangladesh-india-sri-lanka-and-kyrgyzstan/


DFORCE - Intel 8th & 9th Generation computers with Solid State Drives


Tuesday, June 11, 2019

How Hackers profit from your stolen medical data. US to demand 5 years of social media, email info for Visa application

How Hackers profit from your stolen medical data.

Data breaches have become so commonplace that people don't take notice of them as they should.  Everyone is aware of illegal activities associated with stolen credit cards numbers that are used to make forgeries and illegal purchases, stolen ID and SSNs used in identity theft, but of greater value to cyber criminals are information stolen from health care facilities and institutions.

Stolen info based on health care records include not only personal/financial information but insurance documents, stolen doctor licenses, medical diplomas and more

"A hacker compromises the corporate network of a healthcare provider to find administrative paperwork that would support a forged doctor's identity. The hacker then sells to a buyer or intermediary (who then sells to the buyer) for a high enough price to ensure a return on investment but low enough to ensure multiple people buy the item. 

The buyer poses as the stolen doctor's identity and submits claims to Medicare or other medical insurance providers for high-end surgeries." 

The costs are high and only getting worse.  HIPAA was enacted in 1996.  Google, Inc. was founded in 1998.  It could be time to revamp HIPAA and the way our medical information is protected.

Please read more at;  https://www.zdnet.com/article/this-is-how-hackers-make-money-from-your-stolen-medical-data/?ftag=TRE49e8aa0&bhid=27630927001468733386426006914379


US to demand five years of your social media, email account info in visa application

The US State Department will now require new visitors to the United States to hand over their social media account names as well as email addresses and phone numbers used over the past five years.

The data demand will apply to tourists and potential immigrants.

https://www.zdnet.com/article/us-visa-agency-will-now-demand-your-social-media-email-account-info/?ftag=TRE49e8aa0&bhid=27630927001468733386426006914379


Intel Workstations - Solid State Drive based, Gen 8 & 9 Ultra Fast!


Tuesday, May 21, 2019

Microsoft kicks off the rollout of the Windows 10 May Update/1903

Microsoft's Windows 10 May Update/1903 is available to consumers and business customers as of today, May 21. It's available through WSUS, Windows Update for Business and VLSC starting today, too.

Starting today May 21, 2019, consumers and businesses can upgrade to the version 1903, the first feature update to Windows 10 in 2019.  The update is available via download on WSUS, Windows Update for Business.

The latest version available prior to 1903 was version 1809.  You can check which version you are on by using the Windows key + R, the type "Winver" and press the key.  If you are not on version 1809, you can download and install version 1903 without doing the intermediary updates since Windows updates are cumulative.

Users can still delay by 35 days the update however Microsoft is not pushing it on users currently.  Microsoft indicated in April that it was changing the way it rolls out updates to users after the troubles caused by the October 2018/1809 update that caused data loss for some users.

The new update has many new features including "SandBox" which allows Windows Pro, Enterprise and Education users to run potential risky software isolated helping to keep your system safe and secure.

https://www.zdnet.com/pictures/windows-10-update-the-new-features-that-matter-most/16/

I will be updating my system tonight and let you know how it goes.

For the entire story click on the link below;

https://www.zdnet.com/article/microsoft-kicks-off-the-rollout-of-the-windows-10-may-update-1903/?ftag=TREc64629f&bhid=2219791


Wednesday, May 15, 2019

Warning! If You Save your Passwords in a Browser, Don't miss this Blog Post

If you use your favorite internet browsing program to save passwords for websites, you might want to rethink this policy.  This includes all browser programs, Chrome, Firefox, IE and Safari.  In 3 of these, I found the saved passwords were only protected by a user's password or in the case of Safari, the Admin password.  The other major browser has a default policy of no password and will expose passwords with a few clicks of the mouse, however, it does allow you to set a Master password separate from a user password.

If you continue to use this method to save passwords please use a strong password and not one you use for all your protection including websites.  However, if your browser uses a User or Admin password to protect saved website passwords, I have programs that can crack a forgotten password or generate a new password for a user.  In the event your computer is stolen or accessed by a hacker or criminal, they can simply change your password and then proceed to steal your financial website's user name and password.

Lastly, beware this information is readily available using a Googe search.

Google Chrome

I knew about the Password list under settings of Google Chrome but I had never paid any attention to the settings and details of the list.  Last week a client needed to be able to log in to a company web publishing account that was created by a user who had left the company.  I suggested checking if they had saved the account password in Chrome.  Then we could use Chrome to auto login and change the password.  I checked the password list to see if the password was saved.  What I found was that Chrome will easily spill all its content about passwords, Banks, Stocks, Credit Cards, Facebook, any password that is in the saved password list.

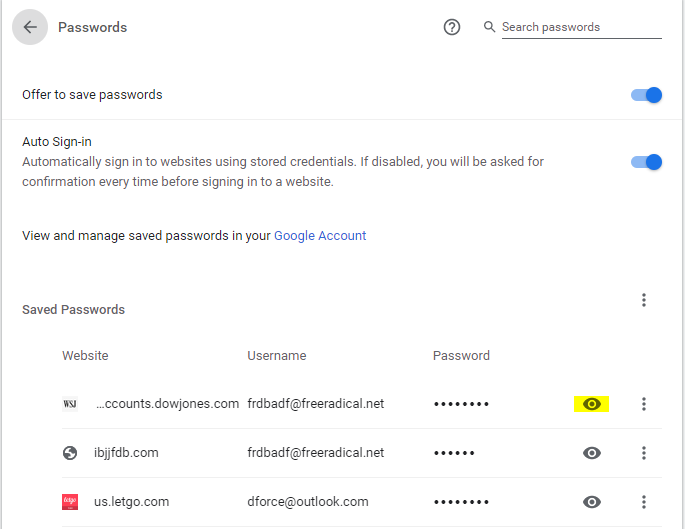
By default, passwords in Chrome's password list are masked by dots to prevent one from seeing the actual password, however by simply clicking on the eye icon next to a password Windows will prompt you for your user login password or pin and voila, all passwords can be viewed by clicking on the eye icon to the right of a saved password.

If you have ever shared your password with a family member, co-worker or haphazardly use easy passwords for protection then any financial, confidential or social media sites you visit that have a saved password can be viewed and compromised.  And let me add this, if I know this then hackers and criminals know this and if your computer is compromised by a trojan or malware then they know where to look to get access to your confidential Financial and Personal information.  These steps are easily found by Googling for the information.

To illustrate how to expose your password info under Chrome, click on the 3 dots in a line, upper right corner of Chrome browser, then select Settings from the drop-down.


Next click on Passwords,


When you do this the saved and not saved Password list appears


Once the list appears, all I have to do is click on the eye icon and the system will respond with the following Window asking for the computer password/pin.


Once you have provided the computer with the correct password/pin, Chrome will then allow you to reveal the hidden password for every saved account.

Below is my IBJJF password exposed (since changed)...


You might think all this is bad enough but no, there's more.

I have a Chromebook and Android phones.  If you have provided your Gmail account to these devices and have Sync and personalize Chrome across your devices turned on, you can go to My Google and find all saved passwords from your Chrome and Android based devices.


Mozilla Firefox and Microsoft Internet Explorer

You may think I'm saying not to use Google Chrome or I am picking on Chrome.  I started with Chrome because it is the most popular Windows Browser now.  However, FireFox and IE both have the same issue.

The default setting for Firefox doesn't require you to provide a password/pin to show passwords.  All you have to do in Firefox is click on the settings icon in the upper right of the Firefox browser, select options,


choose Privacy & Security,


next click on Login & Passwords, Saved Logins.  


click on Saved Logins and you are 1 step away for revealing all saved passwords.

Note:  Mozilla does allow you to "Use a master password" which you will want to do.  This is a better option in my opinion than using the user password for a computer, however as stated this is not the default and Mozilla is wide open otherwise.

Internet Explorer

To accomplish the same feat in IE, go to Internet Tools.  If your browser has the Menu Bar option on simply click on Tools and then select Internet Tools from the dropdown, if you don't see the Menu Bar you can access Internet Tools from the Control Panel.


Next click on the Content Tab and select Settings under AutoComplete


Click on Manage Passwords


To expose a password click on the carat symbol to the right of the password.


As you can see the user ID is already there, you will be asked to provide the user password/pin to reveal the password.


Safari

Apple's Safari browser protects Macs behind the Admin password.  This is only as secure as the password is strong and breakable using 3rd party hacker software.




Tuesday, May 7, 2019

Ransomware, Malware attacks - Protection is important but a Recovery Plan is equally important, Israel responds to Hamas hackers with Air Strike

Ransomware: The key lesson Maersk learned from battling the NotPetya attack

In 2017 Maersk the shipping giant based in Denmark was hit by the NotPetya Ransomware.  Maersk was not an intended target by the developers.  NotPetya was developed by the Russian military and assisted by a leaked version of the NSA EternalBlue Hacking tool which helped to spread the WannaCry ransomware outbreak.  NotPetya's intended target was businesses located in Ukraine, however, it was soon out of control and spreading and causing damage around the world costing billions of dollars in lost revenue and IT costs.

Ransomware and malware require constant vigilance and protection to prevent it from affecting your organization.  With many nation states and their intelligence agencies focussed on cyberwarfare against one another, it is a daunting task.  It was a worm developed by the NSA "Stuxnet" that brought down the Iranian centrifuges in their nuclear laboratories in 2010.  Stuxnet like NotPetya was not contained and soon in the hands of criminal hackers wreaking havoc in businesses around the world.

But while protecting networks and critical systems is the ultimate goal, a data recovery plan must also be in place, so in the event of the worst happening and critical services being knocked out, you can still operate.

A significant part of this, said Woodcock, is "that ability to really understand the core business processes" and know everything about the systems and applications which run the operation.

I personally use redundant backup devices and software at my business clients.  It is imperative that there is also backups kept offline in the event of the malware spreading to the backup devices.

To read more about what happened at Maersk;

https://www.zdnet.com/article/ransomware-the-key-lesson-maersk-learned-from-battling-the-notpetya-attack/

Windows Update:  why it is important to update your systems and computers.  

As new security holes are discovered and exploited, Microsoft releases updates patching these security risks.  Computers that have not been patched or are using an old operating system are targeted by criminal hackers.

NSA's arsenal of Windows hacking tools has leaked

The NSA and other intelligence agencies are also targeting computers around the world.  The NSA used Windows hacking tools to target several banks.

A new trove of alleged surveillance tools and exploits from the National Security Agency's elite hacking team have been released by the Shadow Brokers' hacking group.

The group Friday appeared to release tools designed to target Windows PCs and servers, along with presentations and files purporting to detail the agency's methods of carrying out clandestine surveillance.

https://www.zdnet.com/article/shadow-brokers-latest-file-drop-shows-nsa-targeted-windows-pcs-banks/

In a first, Israel responds to Hamas hackers with an air strike

Three years ago,  NATO proclaimed "cyber" as a target in the modern era creating a new battlefield.  Israel has now been the first to use military force to strike against a foe for using cyber warfare.  Hamas had been engaging in attacks on Israel's cyberspace.  In response, Israel launched an airstrike against as building in the Gaza strip housing Hamas cyber operatives.

"After dealing with the cyber dimension, the Air Force dealt with it in the physical dimension," said IDF spokesperson, Brig. Gen. Ronen Manlis. "At this point in time, Hamas has no cyber operational capabilities."

You don't want to miss this; read more at;

https://www.zdnet.com/article/in-a-first-israel-responds-to-hamas-hackers-with-an-air-strike/

If you are still running Windows XP and Windows 7, look to upgrade today to a new computer.

New DForce Intel 8th and 9th Generations Workstations.


Monday, April 29, 2019

Implantable Medical Devices - keeping them safe from Hackers, also Facebook will be taken over by the Dead in 50 years!

The future of cybersecurity: Your body as a hacker-proof network

Could a 'body area network' be the key to keeping medical devices safe or transferring data between individuals?

Modern medicine is making use of the internet with more devices having internet connectivity.  Insulin pumps, pacemakers, and more implantable devices are being fitted with wireless internet connectivity that allows doctors to monitor your health remotely.

The issue with being connected to the internet is that the devices can be hacked.  Already proof of concept attacks has illustrated the risk exists.  Fortunately, there have been no attacks so far but cybercriminals have demonstrated a lack of morality and tampering with these devices will no doubt happen.  In the past, they have extorted hospitals putting patients at risk.

The wireless technology used to share data can be read many feet away.  Recently implantable defibrillators were given a severity rating of 9.3 out of 10 for a flaw that allowed them to be hacked 20 feet away by the Department of Homeland security.

Scary stuff but new research using the human body as the signal carrier restricts the signal to a few centimeters outside the patient.  Researchers at Purdue University have created Electro-Quasistatic Human Body Communication (EQS-HBC) which uses low-frequency, carrier-less broadband transmission.

To read the full article click on the link below.

https://www.zdnet.com/article/the-future-of-cyber-security-your-body-as-a-hacker-proof-network/?ftag=TRE49e8aa0&bhid=27630927001468733386426006914379

The dead will take over Facebook in the next 50 years
Analysis suggests that the deceased will soon outnumber the living on the network.

and I thought it was me the reason no one responded to my posts.  :-)

A time is coming in which you may see more memorial accounts on Facebook than active users, with academics estimating that accounts belonging to the deceased will outnumber the living within 50 years.

https://www.zdnet.com/article/the-dead-will-take-over-facebook-in-the-next-50-years/?ftag=TRE-03-10aaa6b&bhid=2219791


Tuesday, April 16, 2019

Ransomware: The cost of rescuing your files is going up as attackers get more sophisticated

The average ransom demand is up to almost $13,000, compared with $6,700 just a few months ago.


The sharp increase in ransom payments is linked to the emergence of more expensive and more hands-on forms of ransomware like Ryuk, Bitpaymer and Dharma.

While ransomware attacks of the past generally relied on spamming out large numbers of phishing emails in the hope of getting a few hits, now cyber criminal groups are taking a more focused approach with attacks.

They are now attacking computers directly across the internet.  The new forms of ransomware rely on more direct attacks on computers.  They are exploiting security holes in remote desktop protocols (RDPs) to gain access to systems and once in they are attempting to infect and encrypt as many computers as possible on a network.  That is why it is so important to install updates on your system and not to use outdated operating systems that are no longer supported by manufacturers, see prior post below.

https://dforceatl.blogspot.com/2019/04/windows-updates-problems-and-new.html


Office 365 users are targets of phishing attempts attempting to steal their credentials.  It is easy to copy the underlying source code of a website, Office 365 portal for example and then publish it to create a fake website that looks like the genuine site (you must pay attention to URL).  The target will receive an email allegedly from Microsoft threatening to close the account unless action is taken.  The link to the phony site will then ask for your email and password.  If the info is supplied, the attacker will then take charge of your account, encrypting OneDrive, Sharepoint and using the compromised email to send phony financial documents and other attachments which will appear to come from a trusted source by the recipients.  Be careful.

If you are a victim of ransomware, the attackers can command ransom payments of six figure sums – which attackers demand in cryptocurrencies like Bitcoin.

While the authorities generally don't recommend that victims of ransomware attacks pay the ransom demand – it funds criminal activity and there is no guarantee it will work anyway – in some cases, organizations feel as if they don't have a choice.

It was last month that I wrote about Jackson County, Georgia paying $400,000 to criminals that had infected it's systems with ransomware.

https://dforceatl.blogspot.com/2019/03/georgia-county-pays-400000-to-hackers.html

To read more about the threats, use the links below.

https://www.zdnet.com/article/ransomware-the-cost-of-rescuing-your-files-is-going-up-as-attackers-get-more-sophisticated/

https://www.zdnet.com/article/ransomware-an-executive-guide-to-one-of-the-biggest-menaces-on-the-web/

Friday, April 12, 2019

Windows Updates - problems and new Feature Release 1903 due soon.

Since Windows as a Service (SaaS) became the norm with the introduction of Windows 10, Microsoft has been making changes to the way it rolls out updates to end-users to keep the OS up to date.

The update process has not been a smooth one.  Microsoft's VP of Windows last week acknowledged that updating can be "disruptive".  It was in October of 2018 when Microsoft rolled out version 1809 and many users found that their files had been deleted due to a bug.  I'm not sure if the bug was part of the update or the new OS itself but Microsoft halted the update for 6 weeks until the issue had been resolved.

It's not an easy task for Microsoft.  There are over 800 million PCs running Windows 10 worldwide.  Unlike Apple which controls every facet of their products, there are hundreds if not thousands of PC hardware manufacturers.  Since some make only components to be used in a finished PC, this leads to innumerable variations in hardware.  Add to that all the available software that can be installed and user personalization that makes anticipating every outcome difficult if not impossible.

It is important that you update your Windows to ensure that security holes and bugs have been patched.  Not doing so leaves your computer exposed to hackers and criminals who are always evolving as well as the tools they use to attack your system and steal your data.

There is a new feature coming with the next Windows feature release called "SandBox" that will allow your computer to run in a secure lightweight environment to protect your computer from Malware without affecting the normal Windows installation.  Believe me, you will want this.

There are major updates available now for Windows version 1809 and we are on the cusp of the first major Windows feature release of 2019, version 1903 due for release any day now.

https://medium.com/@win10tricks/windows-10-1903-april-2019-update-release-date-new-features-and-improvements-f49953f6f595

If you are unsure which version you are on, execute the command "Winver" in the Search Box


or use run (Win +R), then type Winver.  Your version will appear similar to below;


to read more, check the links below and Thanks for reading!

https://www.zdnet.com/article/windows-10-updates-why-microsofts-battle-isnt-over-yet/


Microsoft's April Patch Tuesday comes with fixes for two Windows zero-days

https://www.zdnet.com/article/microsofts-april-patch-tuesday-comes-with-fixes-for-two-windows-zero-days/?ftag=TRE-03-10aaa6b&bhid=2219791


Windows 7 problems: Microsoft blocks April updates to systems at risk of freezing

Microsoft has blocked this week's monthly and security-only Windows 7 and Windows 8.1 updates for Sophos antivirus users after widespread reports that computers failed to boot after installing them. 

The problems are caused by Microsoft's Tuesday Windows 7 and Windows 8.1 monthly rollup and security-only updates KB4493467, KB4493446, KB4493448, KB4493472, KB4493450 and KB4493451. 

https://www.zdnet.com/article/windows-7-problems-microsoft-blocks-april-updates-to-systems-at-risk-of-freezing/?ftag=TRE-03-10aaa6b&bhid=27630927001468733386426006914379

https://www.forbes.com/sites/daveywinder/2019/04/12/microsoft-confirms-latest-updates-are-freezing-windows-heres-how-to-fix-it/#4e025fb84d99


New Intel 8th and 9th Generations Workstations.


Wednesday, April 3, 2019

GA Tech 1.3 million data breach, Albany NY, latest victim of Ransomware. Is your Office 365 OneDrive and SharePoint safe?

Potentially 1.3 million current and former students affected by Georgia Tech data breach

Although world renowned for its computer science programs, Georgia Tech has exposed the second data breach to occur at the school in less than a year.  The news was announced yesterday and the potential fallout of exposed names, addresses, SSNs, and birth dates could affect 1.3 million current and former students.

Read all the details in the following link;

https://www.ajc.com/news/breaking-news/breaking-data-breach-exposes-georgia-tech-faculty-students/zAUUNWy5hoHQ8bNvMxcsWL/

New York capital hit by ransomware attack, taking services offline

Albany, NY is just the latest city to become a victim of ransomware, the city announced Saturday, 03/30/19.  City services impacted so far is limited to its ability to offer birth, death and marriage certificates.  People seeking these services are having to visit state vital records offices.

Albany police are said to have no access to any service or program that relies on internet connection.
The situation is still being assessed and inquiries to the Mayor's office on Monday were not being responded to.

Ransomware attacks on cities have been increasing due to lax security and that the attack is more likely to be successful.  Citizens depend on city government services thus city official feel more pressure to resolve the situation.

Gregory McGee, the Police union's vice president, said that the ransomware was also affecting computers in patrol cars related to "incident and accident reports."  "One has to ask the question of why a police department with sensitive information is on the same network that was so easily attacked."

In March of 2018, Atlanta, GA was targeted.  City officials refused to pay and recently the ongoing recovery process has been estimated to cost $17 million.

Two Iranian hackers have been charged by the Justice Department with using malware to attack targets with critical infrastructure or that offer critical services.  Hospitals have been targetted and in many cases, the victims could not pay but the alleged hackers have still taken in $6 million.  The Iranians remain at large since there is no extradition treaty with Iran.

https://www.bleepingcomputer.com/news/security/new-york-albany-capital-hit-by-ransomware-attack/

https://www.cnet.com/news/new-york-capital-hit-by-ransomware-attack-taking-services-offline/


Office 365, OneDrive and SharePoint folders.  Are you safe from Ransomware?

Many companies today have Office 365 and use OneDrive and Sharepoint to synchronize their onsite server and Cloud services.  This is a backup in the traditional sense.  However, ransomware encrypts the files on your system, rendering them unusable.  They cannot be opened or viewed without the key to decrypt them.  Hence the term ransomware because the attacker generally will request a payment be made in cryptocurrency to obtain the key.

If your server or computer is attacked by ransomware and it syncs with your cloud then it will overwrite the files in the cloud.  Fortunately, OneDrive has a feature called versioning.  Up to 50 previous versions of any Microsoft Office file exists and you can revert to the good version that was overwritten.

Unfortunately, this works only for MS Office files.  Ransomware will encrypt jpegs, PDFs and all files located on a computer.  So all non-related Microsoft Office files are subject to be lost.  It will also be time-consuming and troublesome to have to reversion all your Office data.

It is therefore imperative that you keep multiple day backups of your data.  You should keep multiple days in case the attack happens and goes undetected for a day or two.  If you have only a single day backup, say the same backup occurs to the same external drive daily and you get attacked, you could end up with a backup of the encrypted data.

Redundant backups are a good insurance policy in the event of a Malware attack.  Hardware failure is no longer the main threat to your data.  Organizations and staff must protect against the constant threat of malware and ransomware in today's IT climate.  A good backup plan is essential to safeguard your data.

Start examining your backup and security needs today before it's too late.


Support for Windows 7 ending 01/14/2020.

If you are still using XP based systems then there has not been any security patches or updates to your computer since 04/08/2014.  Experts agree that you should not use Windows XP based computers to access information and email on the internet.  There aren't any modern browsers or AV software for these computers available any longer and the risks to your data and personal info is exponential.

In approximately 8 months support for Windows 7 ends.

Plan today to upgrade your systems to a new DForce Intel based computer with the newest Generation 8 and 9 Intel processors running Windows 10.


TEST